Toolwarrant is an offline permission-design desk for developers, security reviewers, technical leads, and teams deploying tool-using AI agents across files, shells, cloud APIs, messaging, and business
Toolwarrant is an offline permission-design desk for developers, security reviewers, technical leads, and teams deploying tool-using AI agents across files, shells, cloud APIs, messaging, and business systems.

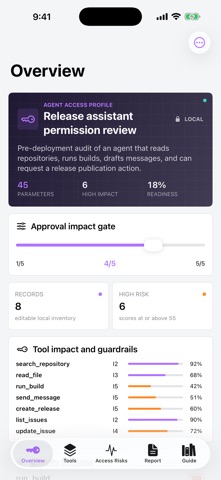
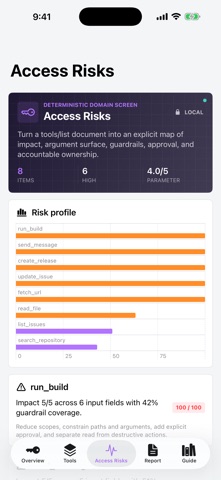
Turn a tools/list document into an explicit map of impact, argument surface, guardrails, approval, and accountable ownership.

KEY FEATURES
- MCP tools/list JSON import
- Impact and parameter-breadth model
- Read-versus-write separation
- Approval and path-scope register
- Dangerous-operation screening
- Owner and guardrail evidence
- Least-privilege profile export
- No model or server connection
- Native structured-file or CSV import
- Local PDF, workspace JSON, and domain-artifact export
- No account, ads, analytics, tracking, IAP, or subscription

Toolwarrant reviews declared tool metadata and human-entered assumptions; it does not execute tools, inspect server code, enforce policy, or guarantee agent safety. Validate authentication, scopes, runtime isolation, prompts, arguments, side effects, logs, and approval behavior in the real system.